
Security Is No Longer Someone Else's Problem
요약 · Summary
$6.36 billion left Binance in about 20 minutes, and Binance says no private key leaked. Crypto looks for safety in cryptography, but people are the weak point. The more our assets go digital, the more security starts to look like defense.

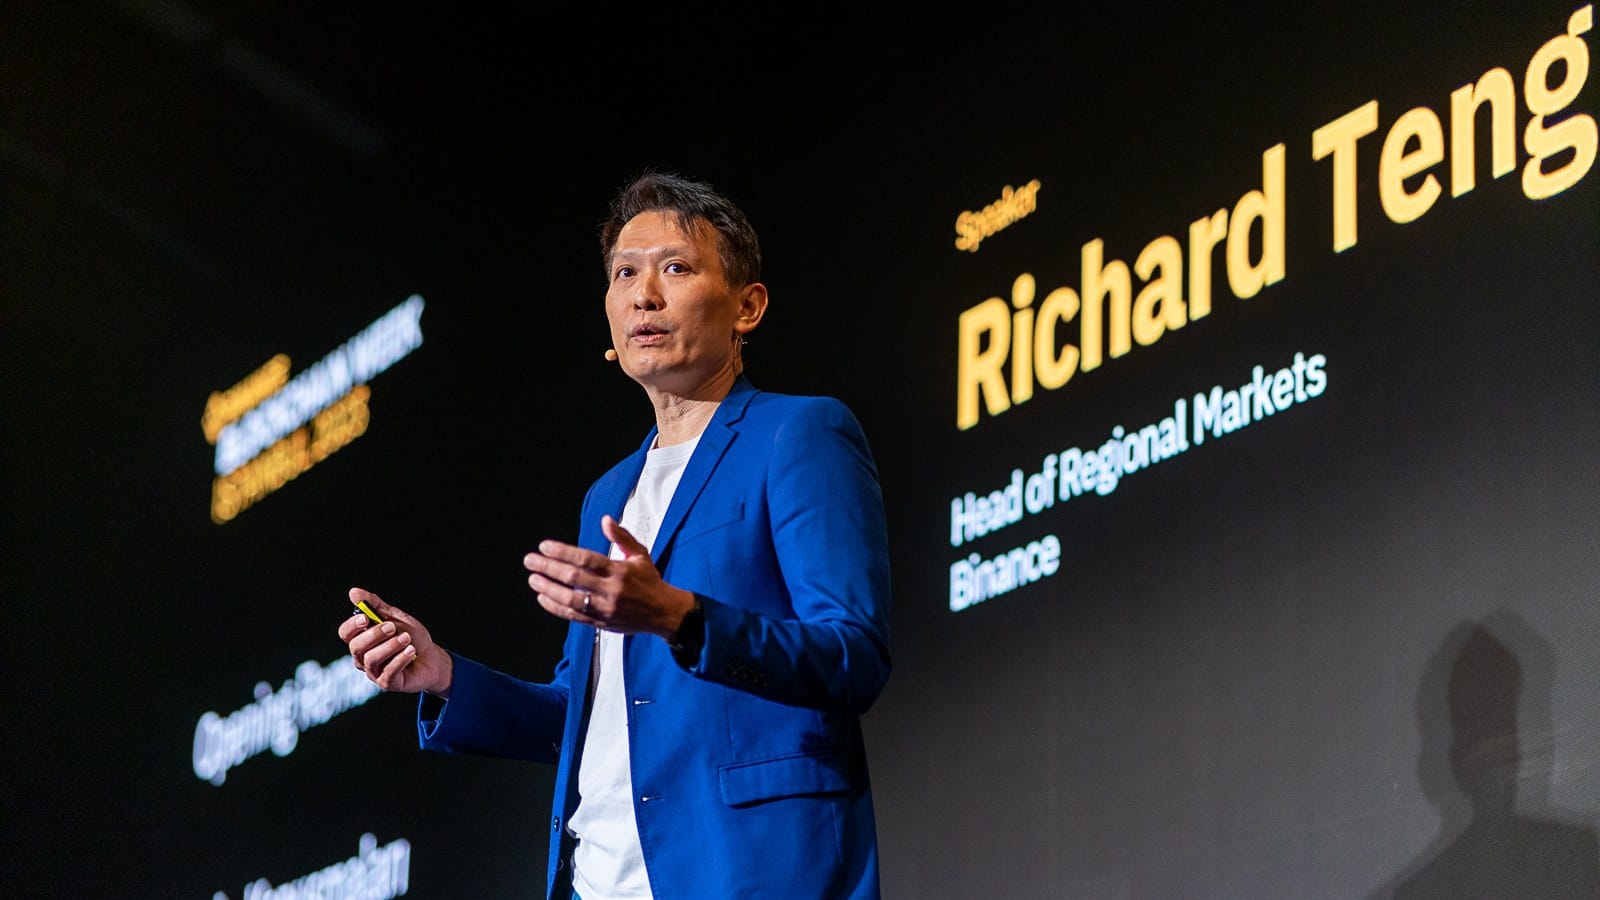
On October 29, about $6.36 billion left Binance's hot wallets across ten blockchains, most of it in roughly 20 minutes. It's the largest crypto theft on record, about four times the $1.5 billion Bybit lost in February 2025. TRM Labs attributes it to TraderTraitor, North Korea's top hacking unit. Binance's first explanation was a compromised DevOps engineer's laptop that let the attacker into a service container and submit withdrawals, and it says it found no evidence that any wallet private key leaked. By Friday, CEO Richard Teng said investigators had found "additional points of breach." Binance says it will cover all the losses and is aiming to reopen withdrawals on Sunday.
Exchange hacks aren't new. In 2014, Mt. Gox in Japan shut down saying about 850,000 bitcoins were gone. According to the US Justice Department, hackers had been inside the server holding its wallets and private keys since September 2011, and took at least 647,000 bitcoins by May 2014. Creditors are still being repaid twelve years later; the extended deadline is today, October 31. In 2018, 523 million NEM, about $530 million, left Coincheck, and the company paid back roughly ¥46.3 billion of its own money to 260,000 customers. Korea has been hit too. In 2024, Korean police said the 342,000 ETH taken from Upbit in 2019 (about ₩58 billion at the time) was the work of North Korea's Lazarus and Andariel.
Over time, the attacks have moved toward people. Hackers used to steal keys sitting on servers; now they go after the people who use the keys and the process of signing. The 2025 Bybit hack started when a developer's Mac at the wallet service Safe{Wallet} was compromised. The attackers used it to plant malicious code in Safe{Wallet}'s interface, and Bybit signed a transaction disguised as a routine one. $1.5 billion went out, and the FBI named North Korea's TraderTraitor. Last month Bitget lost $387.5 million after attackers broke two third-party security products and took over internal privileges; again, no private keys leaked. And Binance's $6.36 billion is more than four times Bybit, the previous record.
So where does trust in centralized exchanges go now? To me, this hack makes AI matter even more. Once AI starts exposing the weak spots in the financial systems we already run, every system that's been built has to be checked again. Nobody has shown that AI was used in this attack. Chainalysis only said that thousands of laundering transactions in a short window suggest automation. But the same week, CrowdStrike reported a China-linked group that used an AI attack tool to go after more than 200 organizations in 11 days, with a human stepping in only at the decision points.
Crypto's centralized exchanges had built up a fair amount of trust, and now they're facing a huge crisis. Plenty of exchanges have been hacked this badly and recovered. Binance itself lost 7,000 BTC in 2019 and covered it from its SAFU fund. But those recoveries happened when the market was very good. Now the market is diversifying and slowly maturing, and a lot of Wall Street giants may see this as an opportunity. US exchanges like Coinbase and Kraken, and ICE, the New York Stock Exchange's parent, which has been circling this space for a while, may use this to push deeper into the market Binance held. That very morning, hours before the hack, ICE announced a plan with Trade[XYZ] to bring Hyperliquid-based perpetual futures into a regulated US market, and it's investing in Trade[XYZ]. Earlier this year it invested in OKX, and last year it agreed to put up to $2 billion into Polymarket.
Where do traders go? Broadly two ways. One is somewhere more decentralized, which is why so many eyes went to Hyperliquid. The other is less crypto and more traditional finance or fintech, joined more tightly with blockchain: places that lean on traditional security and still have a central operator. Analysts at Compass Point wrote that the hack could send business to Coinbase and Bullish, and to decentralized exchanges like Hyperliquid, where users trade without handing over custody. Even the market ICE wants to build on Hyperliquid is a regulated one, with know-your-customer and anti-money-laundering checks. But is a decentralized exchange safer? There have been so many hacks there too that there's no safe zone. Countless DeFi protocols have been hacked, and there, when something breaks, nobody can step in to fix it. That's exactly why the BTC and ETH from this hack can't be recovered at all. Tether, Circle, Ripple and World Liberty Financial froze about $2.67 billion in stablecoins, and Arbitrum's Security Council froze 8,426 ETH on its network. But the attacker still holds more than 420,000 ETH and 18,270 BTC, about $2.4 billion that no issuer can touch.
When we're exposed to a big tail risk, we ask, even demand, that a centralized authority step in and set things right, but on normal days we want free, decentralized finance. Crypto maximalists often look for the middle ground in cryptography: find cryptography that hackers can never get through, and you're done. But that isn't where the problem is. People are the biggest weakness. Hackers collect the scattered pieces of a person's security from social media, messengers and offline life, and use them to get into that person's computer. A computer is still something each person looks after on their own, and through the gaps in that care hackers take control and work their way, bit by bit, toward the center of the system.
That's what the record shows. The FBI says TraderTraitor's attacks are "often characterized by targeted social engineering directed at multiple employees of the same company simultaneously." In the $308 million DMM Bitcoin theft in 2024, one of them posed as a LinkedIn recruiter and sent an employee at the wallet software company Ginco a malicious Python script dressed up as a pre-employment test. This week, Binance's first suspect was also one engineer's laptop, and the private keys themselves didn't leak.
We need agentic security without that weakness: a security system that takes human weakness out of the loop. Of course, AI has its own problems. Someone could tamper with an agent's own security rules, its AGENTS.md, so that it quietly hands information over to them, or what the agent sees could leak into a frontier lab's model training. But an agent keeps a record of everything, so we can keep improving it, and the improvements add up. Human memory is a deeply flawed system: we remember things in our own favor, or lose the record altogether. Semiconductors make it possible to look back and keep fixing things, permanently.
As tensions around the world rise, we're slowly moving out of an age of freedom and becoming alert to safety again. Things we never used to think about, the safety of our bodies, our assets, our friends' identities, now need protecting.
NATO allies have committed to spending 5% of GDP on defense and security by 2035, and up to 1.5% of that can go to things like protecting critical infrastructure and defending networks. Defense spending is, in the end, money to protect people's physical assets. But most people now bank online, and their assets are managed on digital infrastructure. What's written in that ledger decides what I own. So keeping that ledger safe, exactly as agreed, is how I protect my assets. The further our assets move into digital form, the more we may need to invest in security the way we invest in defense. Or maybe hacking is now a far more cost-effective attack than a physical war. In 2023, Anne Neuberger, then the White House's deputy national security adviser for cyber, said about half of North Korea's missile program was funded by cyberattacks and crypto theft.
Security is no longer someone else's problem. Governments still spend tens of millions of dollars on a single missile; the most expensive US interceptor, the SM-3 Block IIA, costs about $27.9 million each. Hackers take billions with a few clicks, $6.36 billion from Binance alone. Turning every soldier into a hacker might now be the smarter way to attack.
Not investment advice or a price call. The numbers are from the sources below; the reading is mine.
Sources
- TRM Labs: North Korea Steals USD 6.36 Billion From Binance in the Largest Hack in History (Oct 30, 2026)
- Binance: Security Incident Update (published Oct 29, updated Oct 30, 2026)
- CoinDesk: Binance discovers multiple breach points in $6.3 billion attack, eyes Sunday reopening (Oct 30, 2026)
- US Justice Department: Russian Nationals Charged With Hacking One Cryptocurrency Exchange (Mt. Gox) (June 9, 2023)
- The Block: Mt. Gox pushes back repayment deadline by another year (Oct 27, 2025; new deadline Oct 31, 2026)
- Security Affairs: Coincheck to refund customers after cyberheist (Jan 28, 2018)
- Korea Times: S. Korea confirms N. Korea stole $42 mil. worth of cryptocurrency in 2019 (Upbit) (Nov 21, 2024)
- Safe{Wallet}: Statement on Targeted Attack on Bybit (Feb 26, 2025) · Sygnia: Investigation into the Bybit Hack
- FBI: North Korea Responsible for $1.5 Billion Bybit Hack (Feb 26, 2025)
- CNBC: Bitget 'not expecting to recover a lot' from $388 million hack (Oct 2, 2026)
- Chainalysis on X (Oct 30, 2026)
- CrowdStrike: Vapor Panda uses ARTEX to scale a global campaign (Oct 29, 2026)
- Decrypt: Binance hacked for 7,000 Bitcoin (May 7, 2019)
- ICE: Intercontinental Exchange and Trade[XYZ] to Bring Hyperliquid-Based Perpetual Markets Onshore (Oct 29, 2026)
- CoinDesk: NYSE owner takes steps to bring Hyperliquid perpetual futures to U.S. (Oct 29, 2026, with ICE's Polymarket deal)
- CoinDesk: Wall Street analysts on the Binance hack (Compass Point note) (Oct 30, 2026)
- FBI: TraderTraitor responsible for the $308 million DMM Bitcoin theft (Dec 23, 2024)
- FBI: Park Jin Hyok wanted notice
- NATO: The Hague Summit Declaration (June 25, 2025)
- CNN: Half of North Korean missile program funded by cyberattacks and crypto theft, White House says (May 10, 2023)
- Missile Defense Advocacy Alliance: Missile Interceptors by Cost (SM-3 Block IIA at $27,915,625, from the US FY2024 defense budget)
- Chart: hacks and insider thefts only, in dollars at the time, from a chronicle of 61 exchange incidents (2011–2026) built from the sources above plus exchange statements and press reports
새 글을 메일로 받아보세요
한국어, 영어 중 받을 언어를 고르세요. 언제든 해지할 수 있습니다.